
This Stormwatch Monday Open Thread remains open – VERY OPEN – a place for everybody to post whatever they feel they would like to tell the White Hats, and the rest of the MAGA/KAG/KMAG world (with KMAG being a bit of both).
And yes, it’s Monday…again.
But we WILL get through it!
We will always remember Wheatie,
Pray for Trump,
Yet have fun,
and HOLD ON when things get crazy!
We will follow the RULES of civility that Wheatie left for us:
Wheatie’s Rules:
- No food fights.
- No running with scissors.
- If you bring snacks, bring enough for everyone.
And while we engage in vigorous free speech, we will remember Wheatie’s advice on civility, non-violence, and site unity:
“We’re on the same side here so let’s not engage in friendly fire.”
“Let’s not give the odious Internet Censors a reason to shut down this precious haven that Wolf has created for us.”
If this site gets shut down, please remember various ways to get back in touch with the rest of the gang:
- Our backup site, The Q Tree 579486807, https://theqtree579486807.wordpress.com/
- Our old alternative site, The U Tree, where civility is not a requirement
- Our Gab Group, which is located at https://gab.com/groups/4178
- Our various sister sites, listed in the Blogroll in the sidebar
Our beloved country is STILL under DIRECT THREATS by hostile forces – notably COMMUNISTS – and they’re HERE IN AMERICA.
Daily outrage and commie phuckery still abound.
We can give in to despair…or we can be defiant and fight back in any way that we can.
Commies won’t win!
And we will keep saying COMMIES OUT until we get their FRAUD and INSANITY out of our country!
THE STUFF
First America
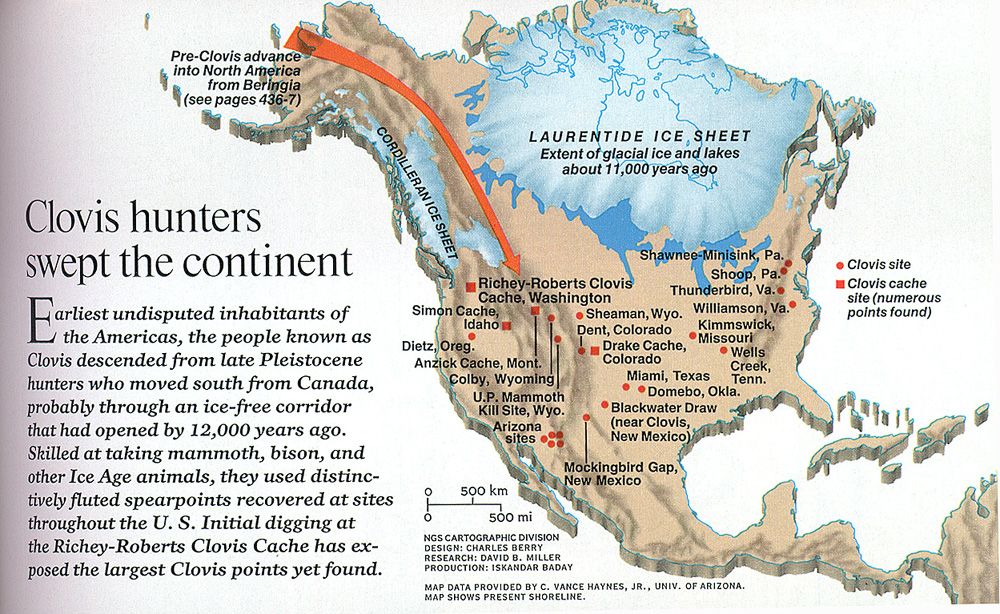
Speaking of Montana, I stumbled into some amazing stories about how American scientists are finally getting some new and improved evidence about the first people to populate this hemisphere.
The first article I ran into was a shorter article in PJ Media, which you can use as a test to see how interested you actually are in this stuff.
The actual article is behind a paywall, so this archive is what you need to check out.
Ancient Human Artifacts Were Discovered in Montana Where They Shouldn’t Have Been
LINK: https://archive.li/GvDeo
If you liked that shorter article, then you will surely want to check out this longer article, in the Montana Free Press. It’s one of the best pieces of science journalism that I’ve read in ages.
‘It should not exist’: Ancient archaeological mystery revealed high in Beartooth Mountains
Young archaeologist digs up evidence that Clovis people lived in Greater Yellowstone high country at least 13,000 years ago — when mountains should have been covered in ice
LINK: https://montanafreepress.org/2026/09/07/ancient-archaeological-mystery-revealed-high-in-beartooth-mountains/
Such a great article. As you can see, there are still surprises out there.
Have a great week, my fellow Americans!
W
And remember…….
Until victory, have faith!
And trust the big plan, too!
And as always….
ENJOY THE SHOW

W




New Schlichter —
https://townhall.com/columnists/kurtschlichter/2026/10/26/trump-needs-a-warrior-for-press-secretary-n2685255
Which, of course, calls for —
I just wish we had one for all the press secretaries….
McEnany’s would be a hoot.
Oh, that never gets old! 😂
“…Kristin sat on my whistle.”
Kristen, dead serious: “I did not do that.” 😂
You know who might be worth a try as Press Secretary? There’s this guy I can’t recall, whose initials are KS……
Don Rickles could have been an incredible Press Secretary. Unfortunately, I believe he’s Taken.
It’s fascinating. And he says there are 30 lifespans of work to be done there. so more discoveries will be forthcoming.
Yup. The “archaeological reserves” are HUGE.
“And he says there are 30 lifespans of work to be done there.”
______________
The best Si models should be able to complete 30 human lifespans worth of work in a few days or weeks, at most.
That’s how the Si models are solving some of the problems, through brute-force deployment of tens of thousands of Si ‘agents’ working 24/7 on the same problem or project, or that’s how I saw it explained, anyway.
Simple.
It’s not over yet.
Bottom line for regular people…
Safest protective thing to do: Reboot your computer. 🕰
The details.
PHP-ocalypse: How two critical web bugs almost broke the internet
https://techcrunch.com/2026/10/24/php-ocalypse-how-two-critical-web-bugs-almost-broke-the-internet/
What’s covered:
Summary.
My normal browser (this one) uses NoScript and doesn’t run on a substantial proportion of websites. One reason I mainly comment here (where I have whitelisted Wolf) instead of Sylvia’s or Marica’s is because I’d have to tweak permissions to do so.
If you’re following closely, you might be thinking, “well, cooth, that blocks client-side javascript….what does that have to do with server-side PHP?”
The answer is that websites are written in PHP on servers, so you pretty much don’t have any client-side PHP interaction — instead, website PHP is modified to dump malignant javascript onto a client…..and that’s heavily filtered on this system.
You are the least likely to have trouble, but for most people, a full reboot of the computer clears session credentials that may have been swiped by malware and that is pretty important.
For session credentials, I also go crude. For interactions with computers where session credentials are a problem (banks, brokerage, credit cards), I use dedicated computers. That way, my browsing to unpatched PHP for “new discoveries in Lake Tanganyika” can’t seize session credentials for Schwab.
In addition, sessions with brokerage and banking sit behind RSA keyfobs — normally used for small businesses, they’re only about $25 to set up.
Remember also that session credentials are only for the session. If you log onto a malware-infested machine and get glommed credentials, rebooting will only dump those, but if you log onto the same malware-infested machine that hasn’t been patched, your new credentials are only going to be glommed again.
Yes, Trump can help by not recognizing Lula’s cheat election.
Interesting curves…..
Ed Martin Says the Lawfare Against Conservatives Is Headed Toward Killing Us
Never give up the guns.
AMEN!
I was remembering a proverb and used Brave search to help me find it:
Prompt: [Hebrew “do not gloat” Bible]
Response:
The Hebrew phrase for “do not gloat” in the Bible primarily uses the verb תִּשְׂמָח (tis-maḥ, Strong’s 8055), meaning “to rejoice” or “be glad,” combined with the negative command אַל (al, Strong’s 408), meaning “do not.”
This specific construction appears in key verses warning against schadenfreude:
Proverbs 24:17: “Do not gloat when your enemy falls” (Al-tis-maḥ bi-s-viv o-yiv-kha).The text advises not to let one’s heart rejoice when an adversary stumbles, warning that God will disapprove and turn His wrath away from the enemy if one gloats.Obadiah 1:12: “Do not gloat over the day of your brother” (Al-te-re or similar forms depending on translation, often linked to אֵיד eid for calamity/distress).This passage commands against rejoicing over the misfortune of Judah or one’s “brother” during their day of ruin.Micah 7:8: “Do not gloat over me, my enemy” (Al-tis-mə-ḥî lî).Here, the speaker asks their enemy not to rejoice over their fall, promising that they will rise again with the Lord as their light.
Scholars note that gloating exposes pride and self-righteousness, placing the individual in the role of judge, which is reserved for God alone.
—
I am guilty.
I repent.
Lord have mercy.
I think gloating leaves the will of God out of the equation. It makes mankind the judge of what should happen to those who strive against us.
On the other hand, there are verses about praising God and thanking Him for defeating one’s enemies. In that case, we may be glad as we give Him the glory for his answers to prayers for deliverance.
My understanding is that it comes down to what is in one’s heart: usurping the role of God, the Judge, vs. praising God for His works.
This is difficult. If someone who has consistently fought against righteous causes, even directly perpetrating evil, becomes too ill to continue their misdeeds, it is human nature to rejoice in their infirmity; but it is another thing to rejoice instead that their evil work has been halted. In other words, the focus is on the result (the cessation of evil) rather than having a personal desire that they be harmed. One can pray for healing of their mind, body, and spirit, and for their salvation, while also asking God for deliverance from their wrongs and praising Him for the same.
(Emphasis mine, below.)
Deuteronomy 20:
3 And shall say unto them, Hear, O Israel, ye approach this day unto battle against your enemies: let not your hearts faint, fear not, and do not tremble, neither be ye terrified because of them;
4 For the LORD your God is he that goeth with you, to fight for you against your enemies, to save you.
I don’t see how, in that circumstance, it would be wrong to be glad about the defeat of the enemy and to praise God for the victory.
==================================
Exodus 15
1 Then sang Moses and the children of Israel this song unto the LORD, and spake, saying, I will sing unto the LORD, for he hath triumphed gloriously: the horse and his rider hath he thrown into the sea.
6 Thy right hand, O LORD, is become glorious in power: thy right hand, O LORD, hath dashed in pieces the enemy.
The enemy is defeated. One rejoices, focusing on God and giving Him the glory.
==================================
Psalm 92
9 For, lo, thine enemies, O LORD, for, lo, thine enemies shall perish; all the workers of iniquity shall be scattered.
10 But my horn shalt thou exalt like the horn of an unicorn: I shall be anointed with fresh oil.
11 Mine eye also shall see my desire on mine enemies, and mine ears shall hear my desire of the wicked that rise up against me.
ShoeOnHead is incensed —
An interesting guide to improving your privacy in our digital world.
Beginning Your Privacy Journey (published in 2024)
https://orthopenguin.com/2024/12/16/beginning-your-privacy-journey/
That’s actually not too bad, but for step 1.1 I’m thinking that a picture of a guy tossing the unit off of a 50-foot cliff into raging waves on big rocks is about right.
By which I mean, cellphones are inherently insecure….which is, BTW, why using one for 2FA is stupid. The way most are designed, the cellphone 2FA is actually less secure than a decent login/password.